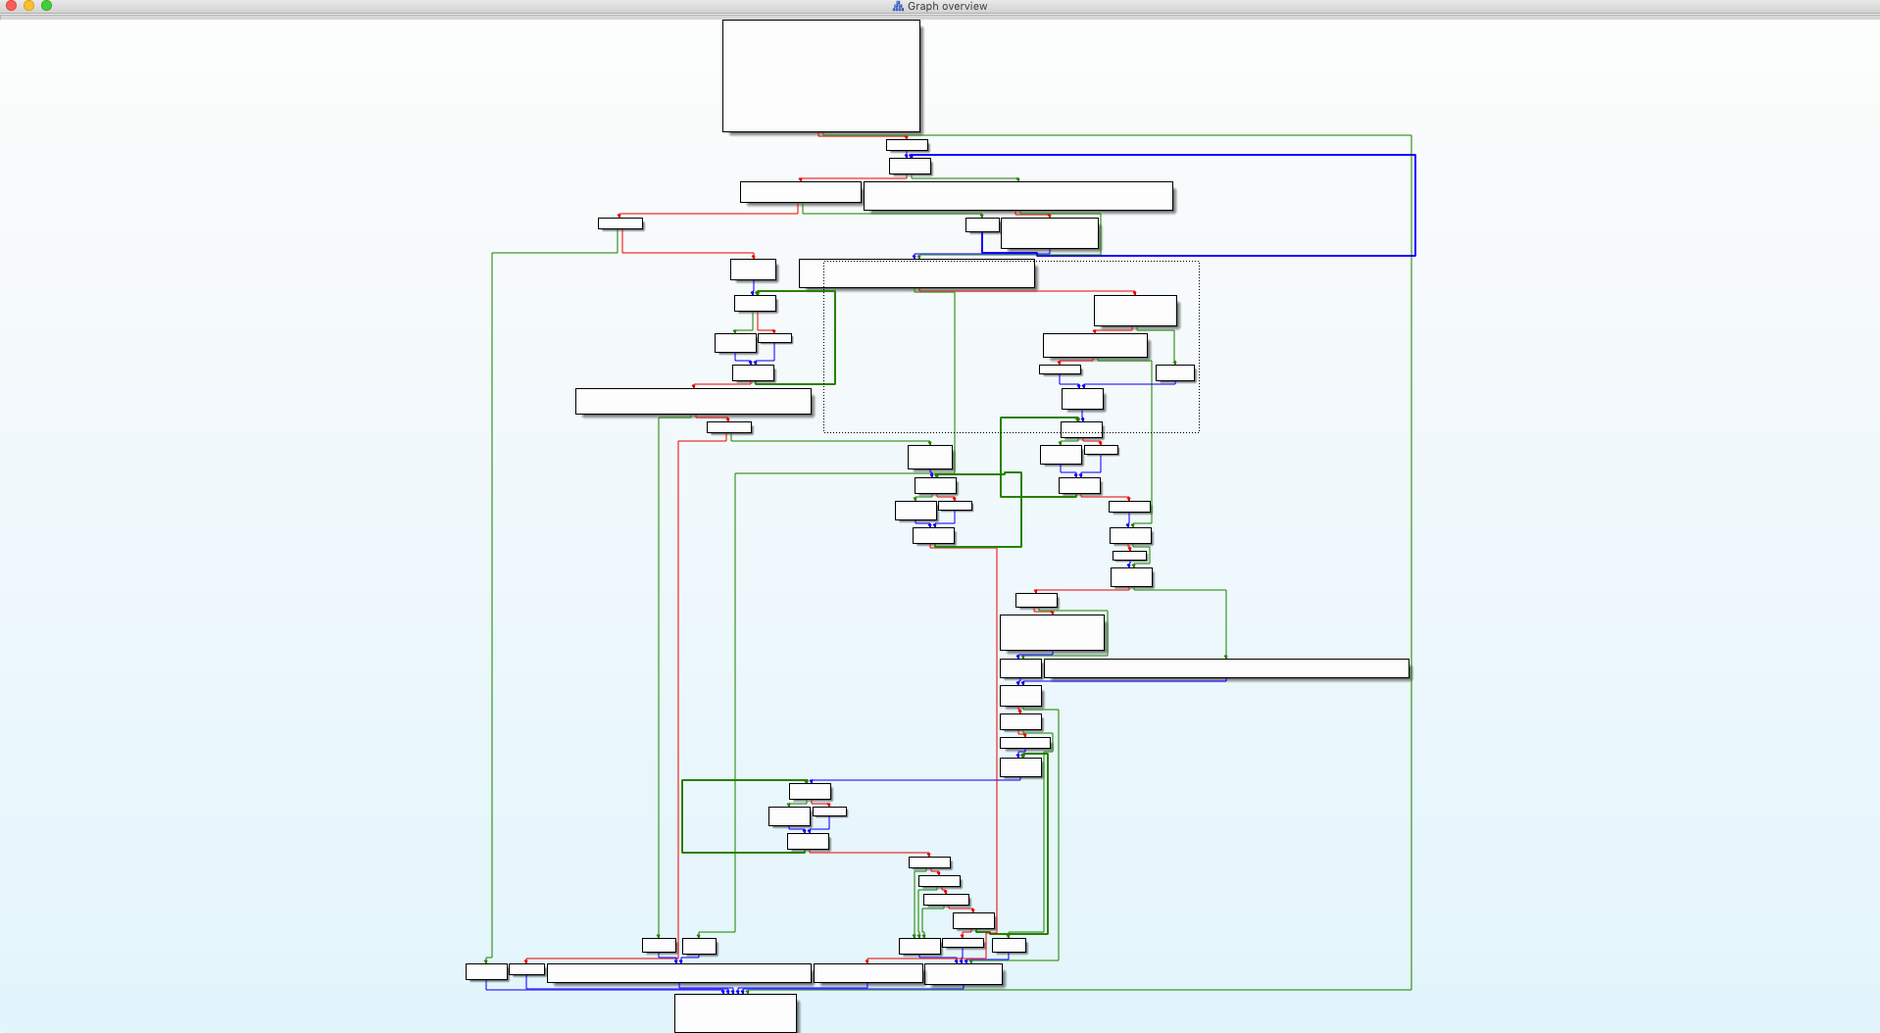
When a binary won't give up its secrets, you need a tool that can lay every instruction bare. IDA Pro is a disassembler, decompiler and debugger that picks apart executables so you can trace logic, audit security or hunt malware.
Interactive Disassembler — what the name IDA stands for. You guide the analysis; the tool follows.
Disassembler — turns machine code into readable assembly across dozens of processor families and file formats.
Decompiler — reconstructs high-level source from binary code, with function type and parameter handling.
Data debugger — built-in, so you can step through code and inspect memory without leaving the workspace.
FLIRT — Fast Library Identification and Recognition Technology. Flags standard library functions so you can skip the plumbing and focus on the custom logic.
Navigation — cross-reference graphs, jump-to-address and search tools built for working through dense, unfamiliar codebases.
Undocumented shortcuts that annotate conditional jumps with one keystroke
IDA Pro hides a few shortcuts that experienced analysts lean on daily — often without the manual ever highlighting them.
- Auto-comment on jump — pressing
;while the cursor sits on a conditional jump auto-generates a comment describing both branches. Tiny keystroke, large payoff when you are tracing control flow. - Stack variable renaming — double-click any local variable inside a stack frame view, rename it, and every reference updates instantly. Much faster than chasing offsets by hand.
- Alt-double-click — on any operand, this jumps straight to the referenced data or code, skipping the graph overview. Keeps your momentum when you are deep in a trace.
- Pasting hex strings — hit
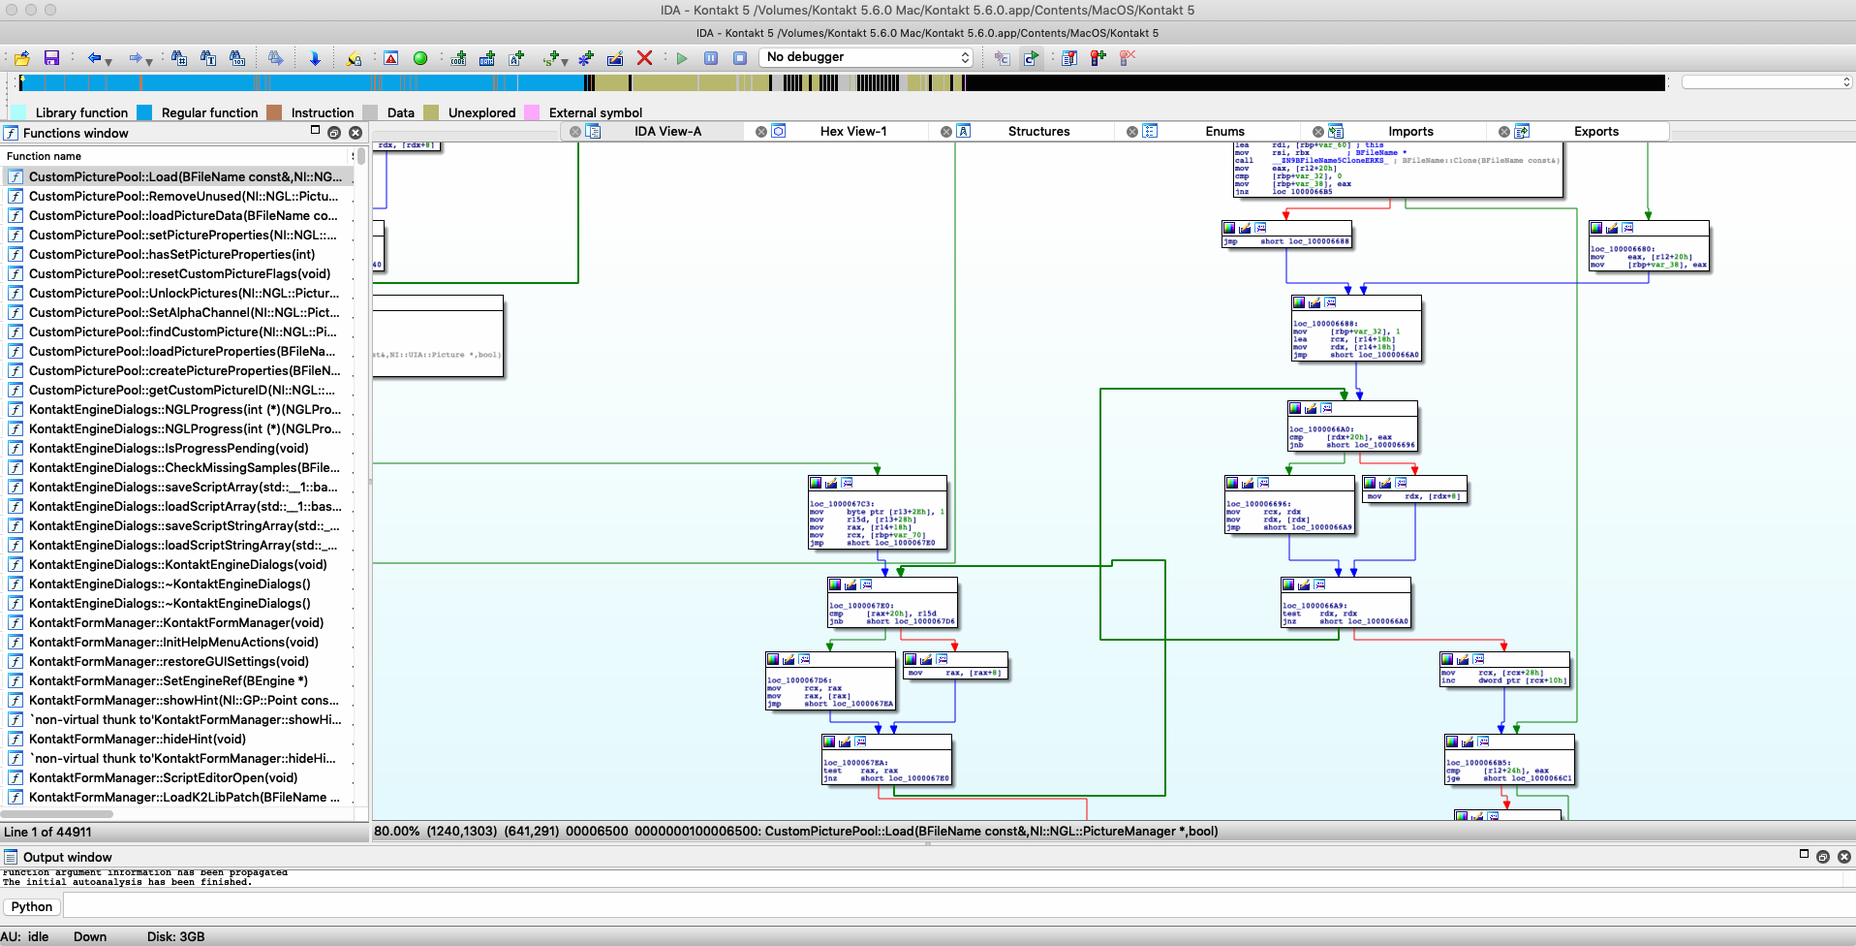
Ctrl+Shift+Gto jump to an address, paste a raw hex string, and IDA converts it to a usable offset. Saves the back-and-forth with a calculator. - Colour bands in graph view — right-click the disassembly graph background and enable grouping by function colour. Blocks from the same function share a tint, which makes spotting inlined code or borrowed chunks far simpler.
FLIRT library recognition silences known code so you zero in on credential logic
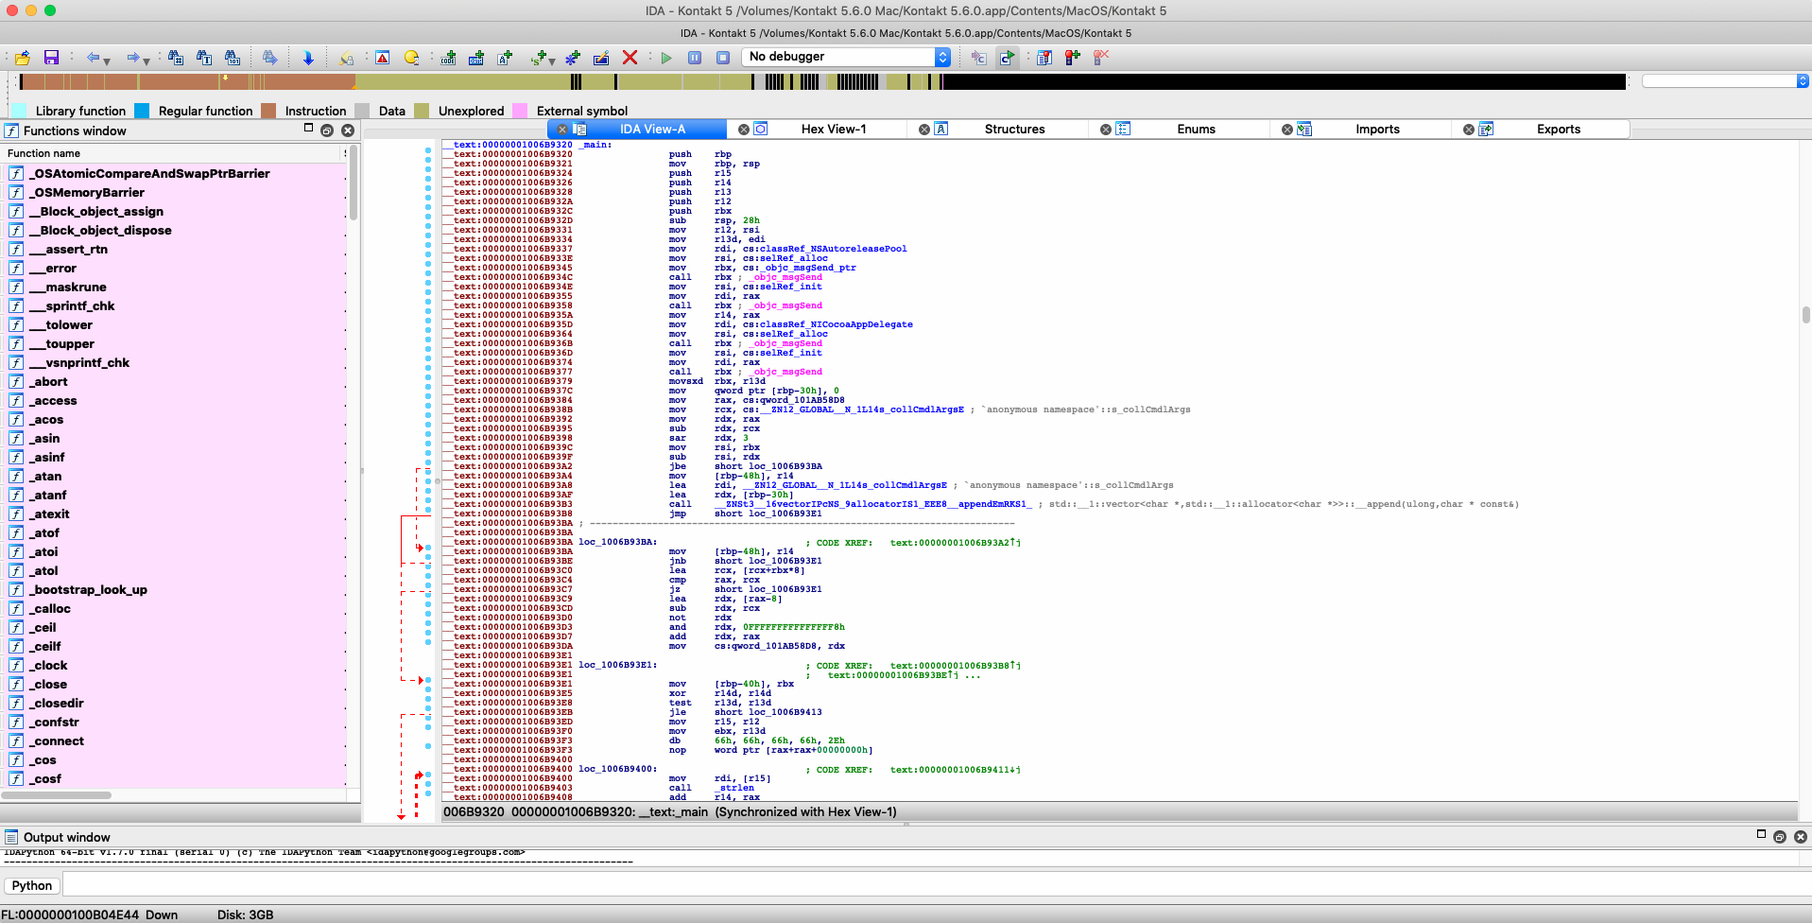
You receive a Mach-O binary from a colleague who suspects credential harvesting. No symbols, no source. You drag the file onto IDA Pro and let the initial auto-analysis run — FLIRT tags known library routines within seconds, greying out chunks of boilerplate code you can ignore.
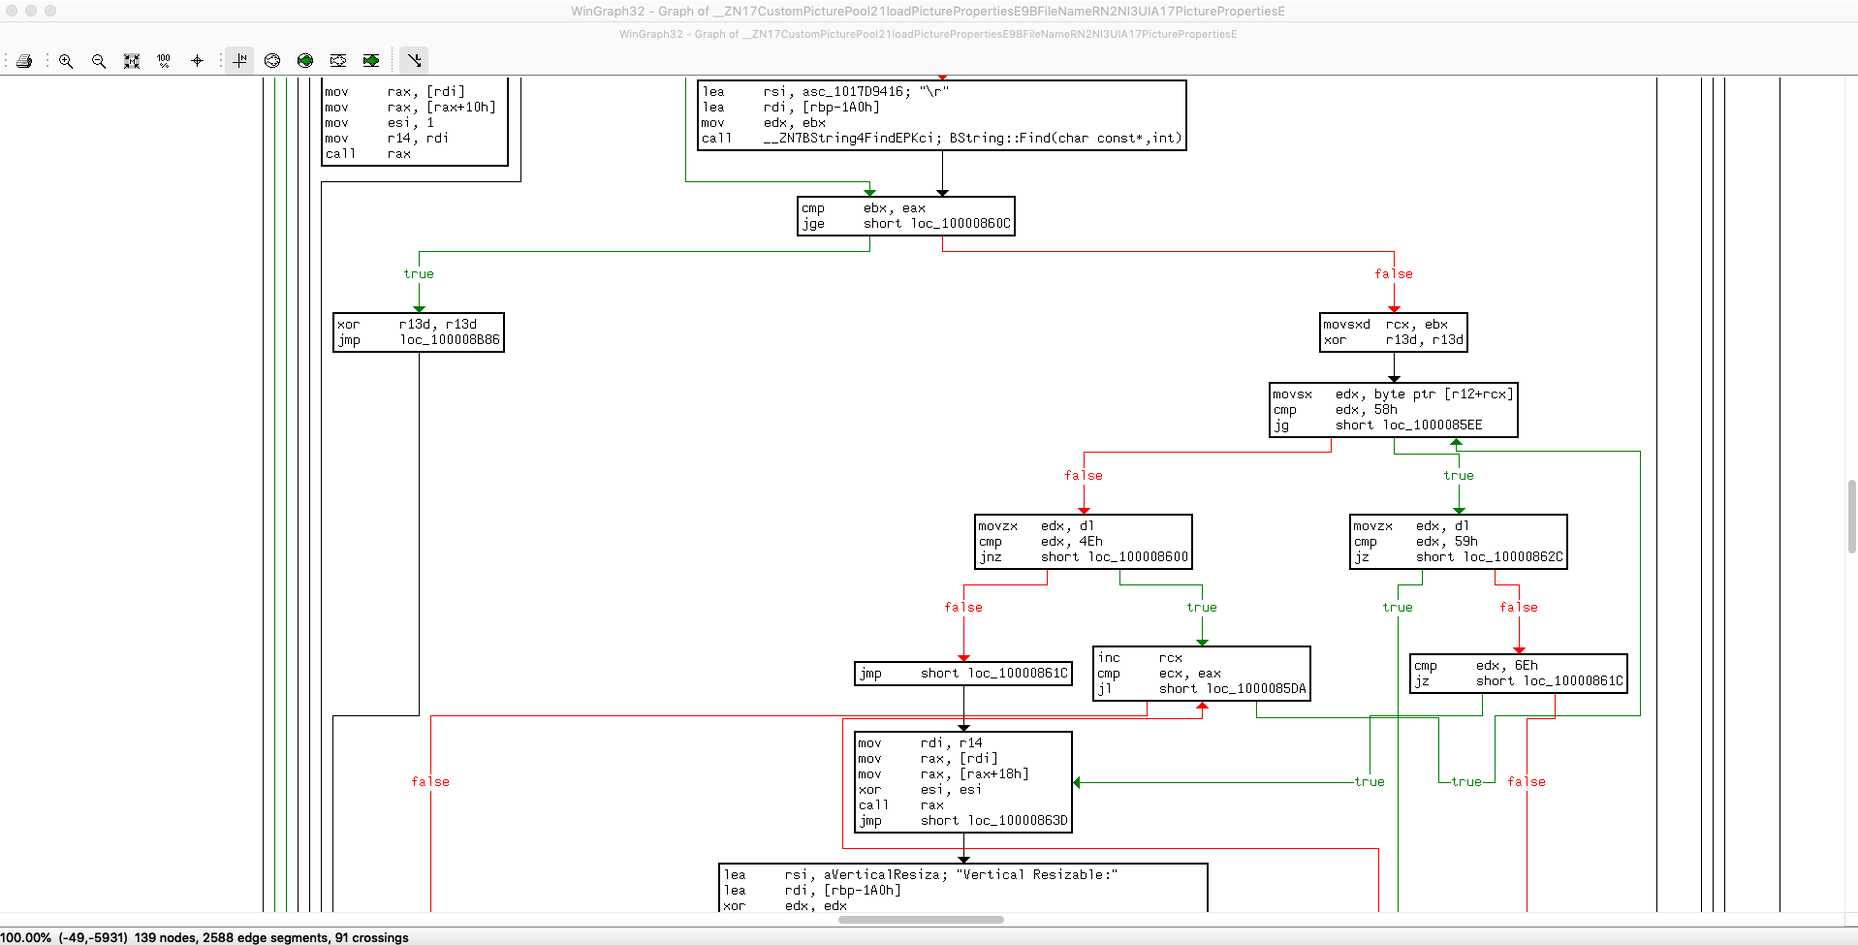
The entry point lands you in the middle of a stripped main function. You press Space to flip from linear listing to graph view. Two conditional jumps branch early; you drop a comment on each with ; and label the likely success path. With the graph laid out, you spot a tight loop around a call to _objc_msgSend — something is iterating over pasteboard items. You rename the function scrape_clipboard and watch every cross-reference update.
You open the decompiler pane and the loop becomes a clean for block. A string reference points to an encrypted buffer. You switch to the Hex View, select the bytes, and use the built-in debugger to set a read watchpoint. Fifteen minutes in, you have identified the exfiltration routine and documented the call chain — without once opening a separate tool.
- New — Dyld Shared Cache infrastructure for analysing Apple's cached system libraries.
- New — Swift analysis improvements.
- New — Pathfinder feature.
- New — Hexagon QDSP6 processor module.
- New — Qualcomm MBN boot-image loader.
- macOS 10.15 or later
- Intel or Apple Silicon Mac
Questions I get before install
What is IDA Pro used for?
Reverse engineering, malware analysis and software security auditing — any task that requires understanding how a compiled binary behaves at the instruction level.
Comments 0
Sign in to leave a comment.Sign inCreate an account
No comments yet. If a step is still there after you install it, say so.
More in Mac Apps
All in Mac Apps iExplorer
Mounts an iPhone or iPad on your Mac for direct file browsing without a jailbreak.
8 steps saved
 Imagenomic Plugin Suite
Consolidates skin retouching, noise reduction, and resizing under one installer.
19 steps saved
 Imagenomic Portraiture
Replaces manual skin retouching with an automated mask-based smoothing engine.
4 steps saved
 iMazing
Backs up, browses and moves iPhone and iPad data without iTunes.
17 steps saved
 Infuse Pro
Plays nearly any video format natively across Mac, iPhone, iPad, and Apple TV.
17 steps saved
 Updated
Hopper Disassembler
Disassembles and decompiles binaries so you can trace logic or audit code.
11 steps saved
 HitPaw Watermark Remover
Traces and removes unwanted objects or watermarks from a single video frame.
10 steps saved
 HitPaw Video Converter
Transcodes files like HandBrake, then adds download, edit, and reframe tools.